Vue.js Studies Day 2 – Getting Started/Installed/Creating an App

I’m going to enumerate these, because holy hell there’s a number of ways to start working with Vue.js. Since I’m time boxing all of the these posts too and study time in a day, it might take more than one post to get through all of these ways to get started with Vue.js.

Method 1 – Hand Crafted Artisanal Vue App

This is the age old approach, and in my opinion one of the best ways to learn something well, to just hand code up a minimal app from scratch. Doing this with Vue is fairly easy, and as with any web application regardless of framework, begins with two files. For these files, we have:

  1. index.html – The index.html file is the standard base file of a web app, or more simply the web site. It’s been the default file that displays for a website since pretty much the dawn of the internet using HTML for composing sites!
  2. main.js – This is the part that initiates the Vue app itself.

Creating the index.html we would need something like this. Note the script file is located on a CDN, and works fine until you don’t have access to the internet (if that were to happen). It’s possible to do the same thing locally by just downloading the vue.js vue.global.js file locally.

<!DOCTYPE html>
<html lang="en">
  <head>
    <meta charset="UTF-8" />
    <title>Minimalistic Vue App</title>
    <script src="https://unpkg.com/vue@3.0.0-beta.12/dist/vue.global.js"></script>
  </head>
  <body>
    <div id="app">
      <h1>{{ appHeader }}</h1>
      <p>{{ appDescription }}</p>
    </div>
    <script src="./main.js"></script>
    <script>
      const mountedApp = app.mount('#app')
    </script>
  </body>
</html>

The JavaScript page, where the invocation of the Vue app is done is loaded via the <script src="./main.js"></script> file, while the Vue framework itself is loaded by the <script src="https://unpkg.com/vue@3.0.0-beta.12/dist/vue.global.js"></script> in the header. Then the app is attached the the div element <dev id="app"> and the elements inside then have various pieces that the Vue framework can then populate based on the capabilities of the framework.

The underlying main.js file looks like this.

const app = Vue.createApp({
    data() {
        return {
            appHeader: 'This is yer Header!',
            appDescription: 'Lorem ipsum dolor sit amet, consectetur adipiscing elit, sed do eiusmod tempor incididunt ut labore et dolore magna aliqua.'
        }
    }
})
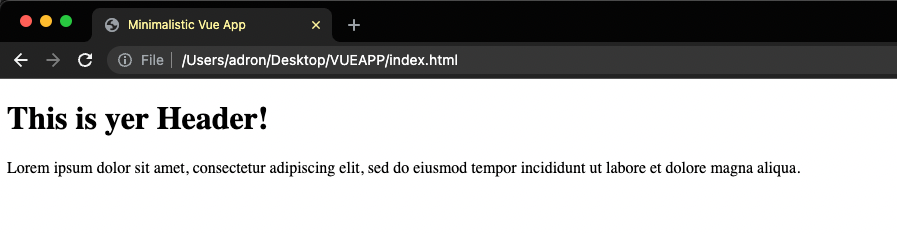
The page displayed.

Method 2 – Creating a Project via NPM

To use this method start by ensuring you have Node.js and npm installed. I use nvm to get these tools installed and manage which version of these tools I have installed, and have detailed what steps I go through here.

Once the prerequisites are installed issue the following npm init command.

npm init vue@latest

That’s it, next you’ll be prompted for all sorts of additional capabilities one can add to a Vue.js App. The easiest however is just to ignore them all, go with the default of No, and then navigate into the directory made for you, install dependencies, and run the app with the following commands. Which mind you, are listed out when you run the above npm init. Working through this automation your terminal would look something like this.
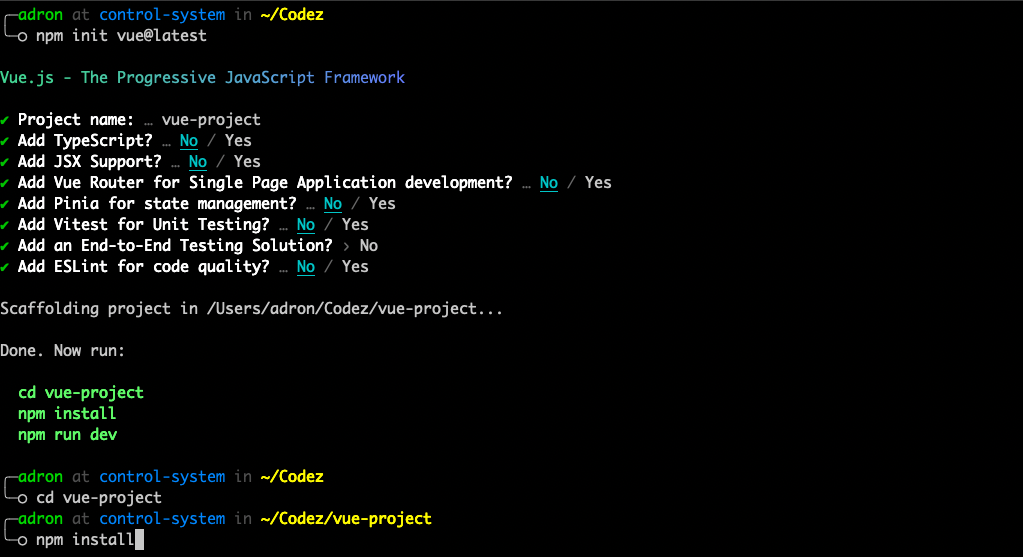
Working through the npm init in the terminal.

Once all that is done, you then npm install and then issue npm run dev you’ll be presented with the following status.
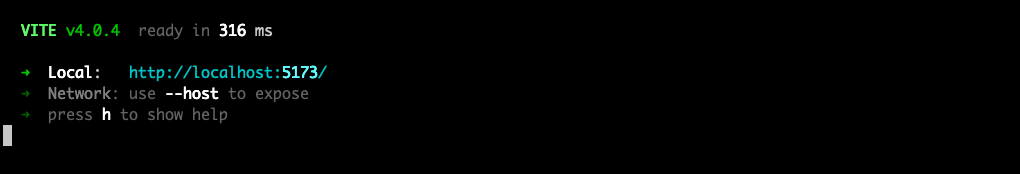
Vite is now running with the default app.

This shows that your app is now running and available via a VITE server that you can open a browser and navigate to http://localhost:5173 to view. That page will look something like this, which is a smidge more shined than a hand crafted artisanal vue app!
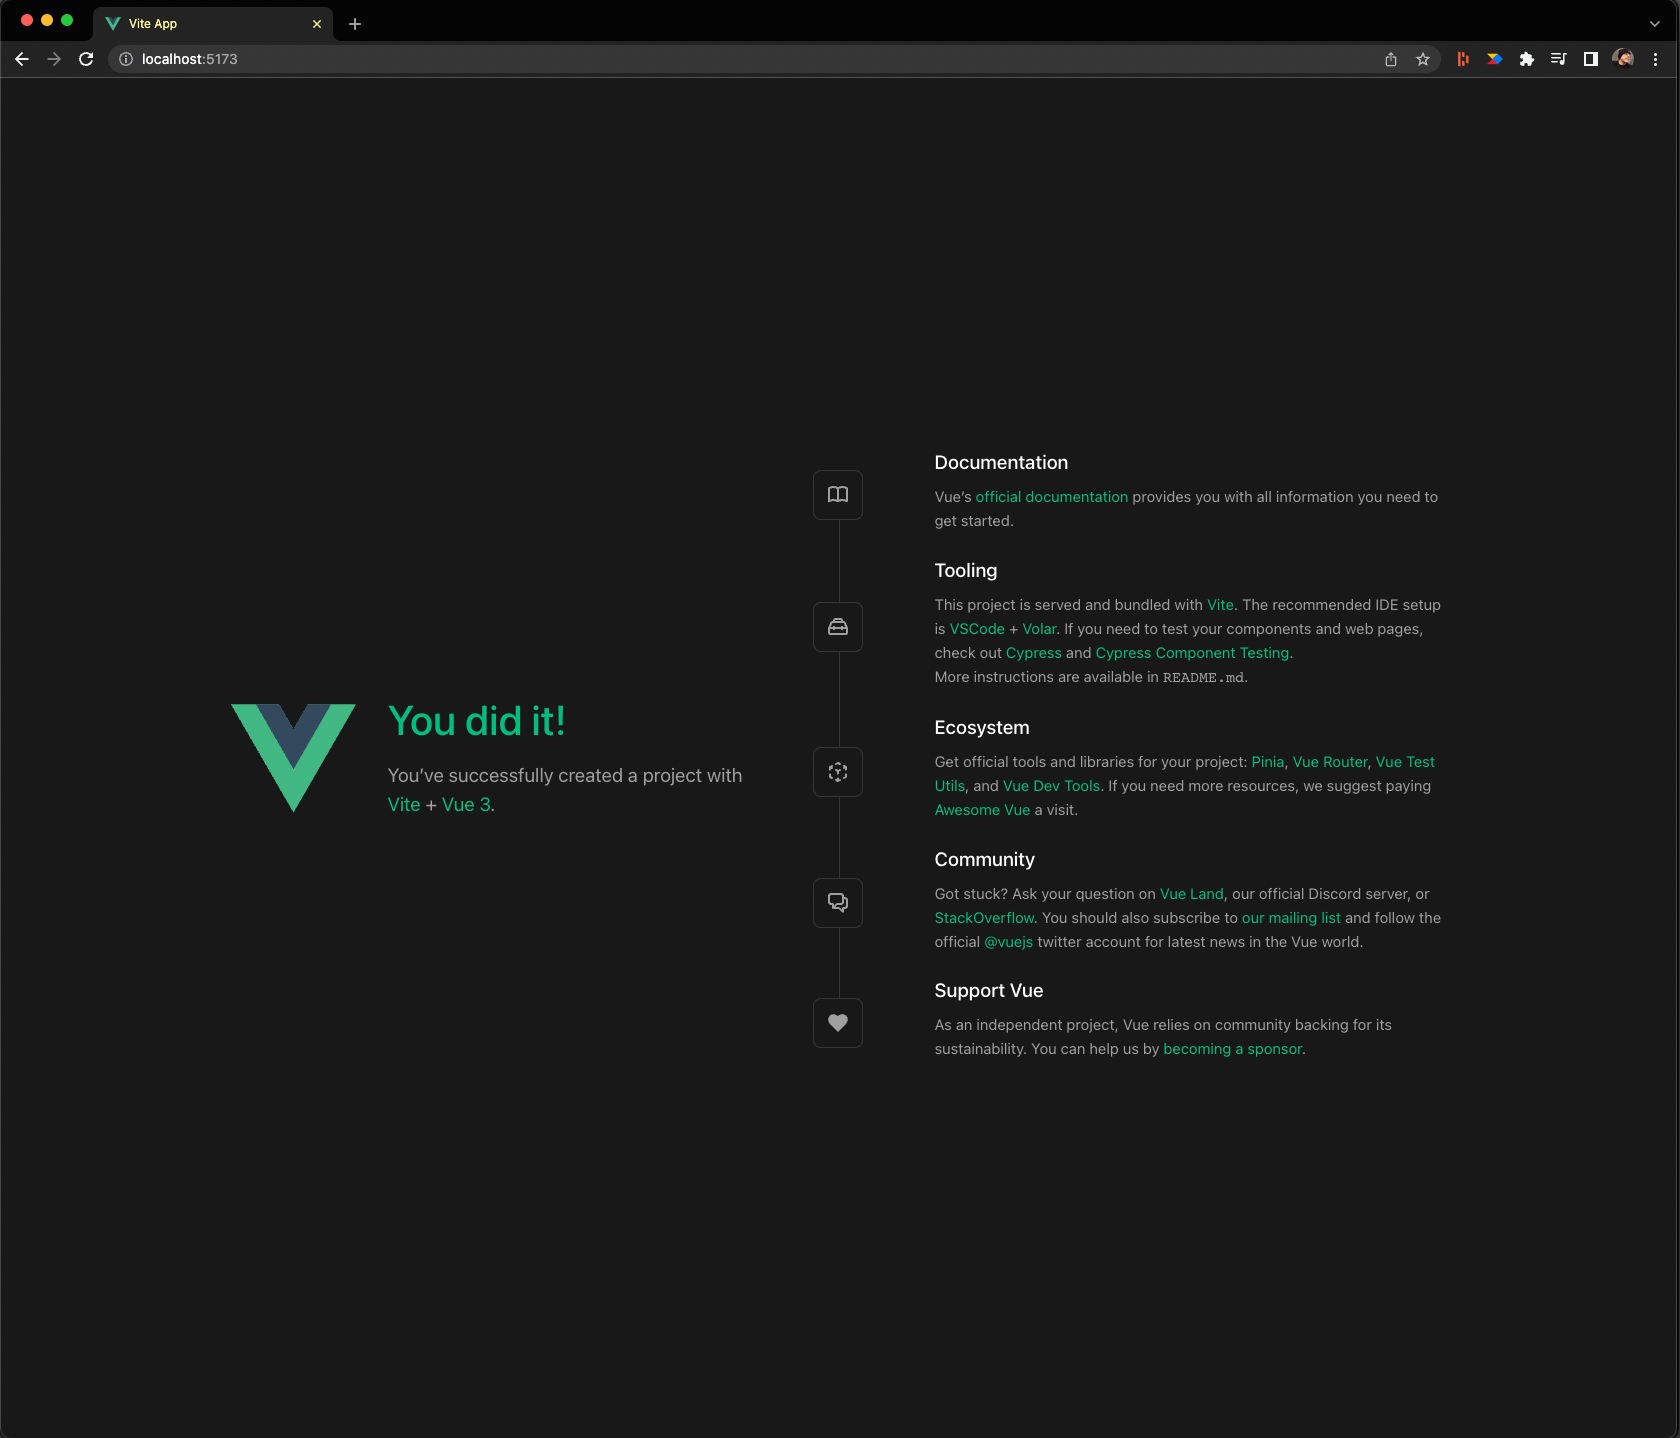
A default vue app when using npm init vue@latest.

That’s it for today’s notes. I spent an exorbitant amount of time toying around with these things so I’ve only gotten through the two methods. But rest assured, these are effective ways to get your vue app started and get going with that initial development.
Vue.js Studies Day 1

I’m putting this core curriculum structure together to accomplish two things.

  1. Learn Vue.js for my own use.
  2. Teach others Vue.js.

The following is my general outline of what I think should be covered for knowledge of Vue.js. I’d love any input, additions, subtractions (i.e. is something not specifically Vue.js related?)

The Vue.js App.

  1. Creating a Vue App.
  2. Features of Vue.js.
  • Declarative Rendering
  • Reactivity Fundamentals
  • Attribute Binding
  • Conditional Rendering
  • List Rendering
  • Event Handling
  • Class & Style Binding
  • Computed Properties
  • Components & Props
    • Registration
    • Props
    • Events
    • Fallthrough Attributes
    • Slots
    • Provide/inject
    • Async Components
  • Communicating Events
  • Form Input
  • Lifecycle Hooks

Vue.js

  • Single File Components
  • Vuex
    • Global State
    • Updating State
    • Fetching State
    • Error Handling
  • Vue Router Essentials
    • URL Parameters
    • Pagination
    • Nested Routes
    • Redirect & Alias
    • Programmatic Navigation
    • Error Handling & 404s
    • Flash Messages
    • In-Comopnent Route Guards
    • Global and Per-Route Guards
  • Axios API Calls
  • Dynanic Routing
  • Deploying
  • Scaling

Unit Testing Vue 3

  • Writing tests with Jest
  • Testing Props & User Interaction
  • Testing Emitted Events
  • Testing API Calls
  • Stubbing Child Components

Vite

  • CSS & Debugging
  • Working with Assets
  • Getting Vite Going

There will be a number of changes to this but the ideas & topical coverage are all there. The ordering will also, very likely, have. a number of changes. For example I’m already thinking that Vite should be up at the beginning of coverage just like the list of ways to get up and running. As I create additional posts on these topics, I’ll link the topics in this post to the topics on the other pages.

JSON Web Tokens

JSON Web Tokens, one hears all about them all the time. But what exactly are they? I’ve used them a thousand times myself but I never really checked out exactly what they are. So this post fills that gap for me, and hopefully it’s useful to a few of you readers out there too.

What is a JSON Web Token?

JSON Web Token, or JWT, is open standard RFC 7519 for compact and self-contained secure information transmission between two parties using JSON objects. For a refresher, JSON stands for JavaScript Object Notation. JWTs provide security between parties by being signed, which can be used the verify the integrity of the claims contained. JWTs can be signed using a secret or a public / private key pair using RSA or ECDSA. JWTs can also be encrypted to hide those claims as well.

What are JWTs good for? When should you use a JWT?

The most common, and what I’ve found the most recommended use of JWTs, is for API authentication or server-to-server authorization.

JWT Structure

Paraphrased and summarized using the Wikipedia example here.

The header identifies which algorithm generated the signature, such as HMAC-SHA256, as indicated in the example below.

{
  "alg": "HS256",
  "typ": "JWT"
}

Then the contenxt, or payload, contains the claims. There are seven Registered Claim Names (RCN) as standard fields commonly included in tokens. Custom claims can also be included, the following is the At Time claim, designated iat and custom claim of loggedInAs. The others include: iss (issuer), sub (subject), aud (audience), exp (expiration time), nbf (not before time), iat (issued at time), and jti (JWT ID). For these and many other claims the IANA has a resource here.

{
  "loggedInAs": "admin",
  "iat": 1422779638
}

The signature securely validates the token. It’s calculated through encoding the header and payload using Base64url encoding per RFC 4648 and concatenated with a period as the seperator. This string is run through a cryptographic algorithm specified in the header (i.e. HMAC SHA 256). A function signature would look something like this.

HMAC_SHA256(
  secret,
  base64urlEncoding(header) + '.' +
  base64urlEncoding(payload)
)

All concatenated together the token would then look like this.

eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9.eyJsb2dnZWRJbkFzIjoiYWRtaW4iLCJpYXQiOjE0MjI3Nzk2Mzh9.gzSraSYS8EXBxLN_oWnFSRgCzcmJmMjLiuyu5CSpyHI

Do and Do Nots

  • Do not use JWTs as session tokens. At least in general, they have a wider range of features and a wider scope. Session tokens are a different beast and using JWTs can increase potential mistakes. Some other issues with this is a JWT doesn’t simply can’t be removed at the end of a session, as it is self-contained without a central authority, and another is that they’re relatively large for such a purpose.
  • Do use JWTs for API Authentication. This is the most common use for JWTs today, as it fits the use case and in many ways was designed specifically for it.
  • Do use a library or some other known way to generate JWT tokens. Don’t just randomly generate a string that looks like a JWT. I’ve seen people just generate a big ole’ wad of text that looks like a JWT before but then it is literally just a big wad of text, you can’t fake a JWT, and in turn when it’s verified or processed by a library for authentication purposes you’ll end up with errors and other issues.

JSON – JavaScript Object Notation

JSON (JavaScript Object Notation), a lightweight data-interchange format. It’s relatively easy to read for us humans, which is nice, and is a subset of the JavaScript Programming Language Standard (ECMA-262 3rd Edition – December 1999).

JSON is a text format, and even though it’s a subset of JavaScript, is language independent. The conventions are of the C-family of languages like C, C++, C#, Java, JavaScript, and others.

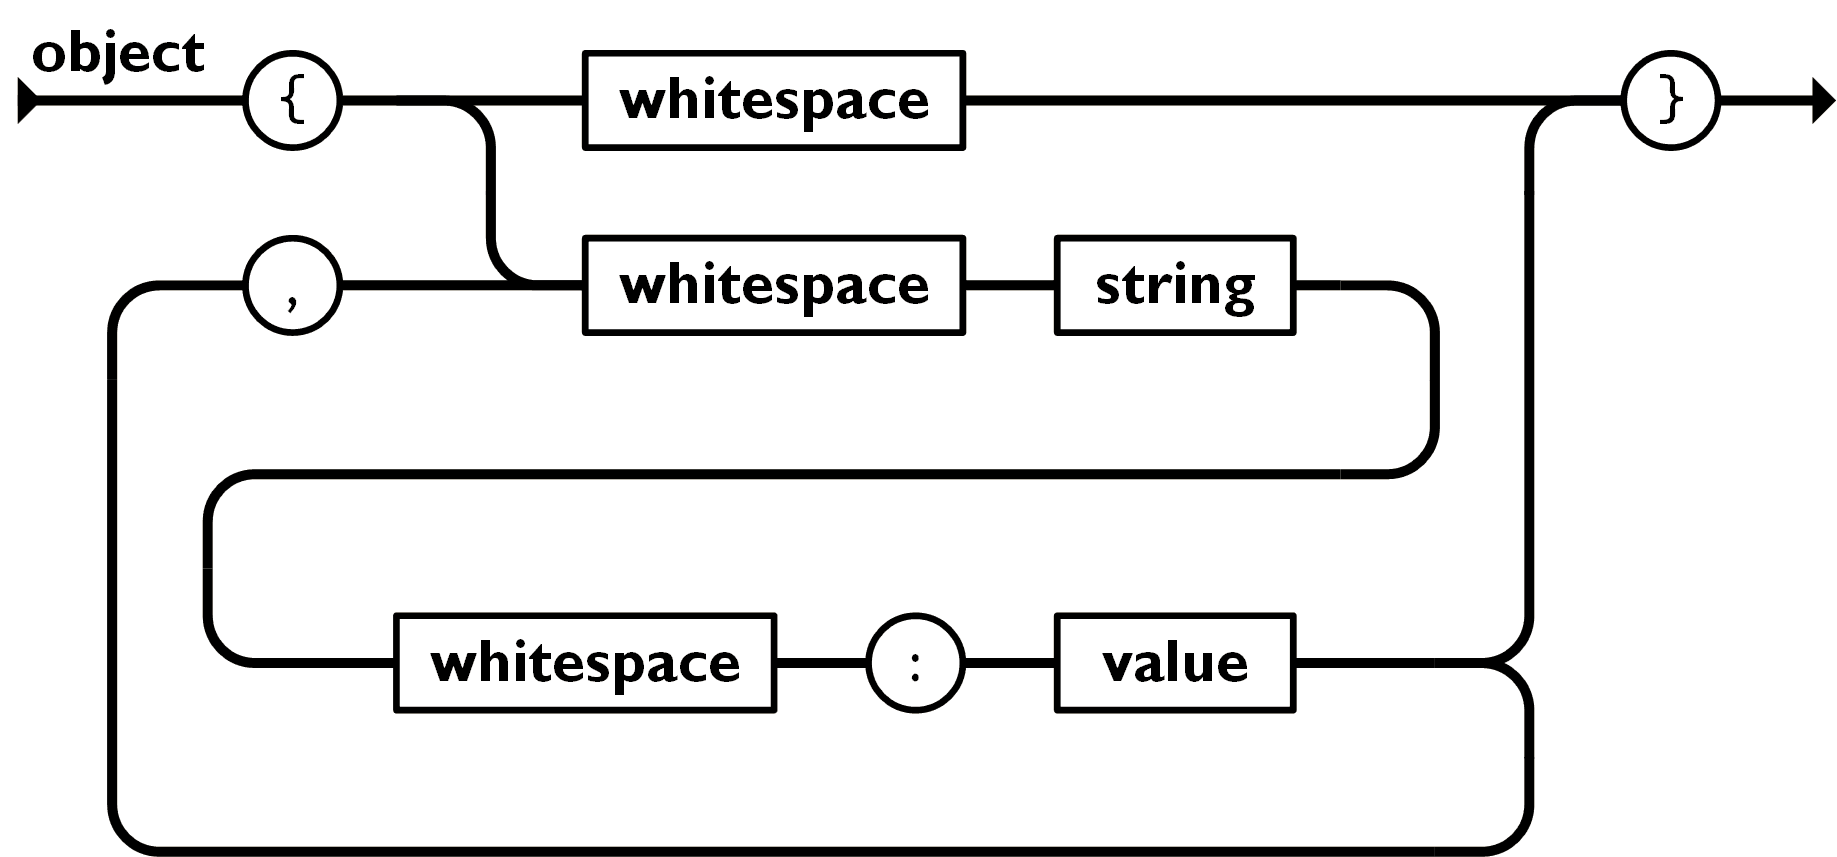
There are two structures to JSON; a collection of name value pairs and ordered lists of values. For more details check out the organization. A few examples for reference.

A simple JSON object.

{
    "name":"John",
    "age":30,
    "car":null
}

An array of JSON objects.

[
    {
        color: "red",
        value: "#f00"
    },
    {
        color: "green",
        value: "#0f0"
    },
    {
        color: "blue",
        value: "#00f"
    },
    {
        color: "cyan",
        value: "#0ff"
    },
    {
        color: "magenta",
        value: "#f0f"
    },
    {
        color: "yellow",
        value: "#ff0"
    },
    {
        color: "black",
        value: "#000"
    }
]

A JSON object using a list.

{
    "name":"John",
    "age":30,
    "cars":["Ford",&nbsp;"BMW",&nbsp;"Fiat"]
}

Choosing Circles

Mastadon

With Twitter under new management combined with the urge to leave over the last number of years, I’ve left my account and moved to a more specific circle of connections on metalhead.club as me @adron@metalhead.club. If you want to keep receiving my feed of this and that; tech, bicycle, train and travel, heavy metal, war related tweets – at least until Russia is defeated and removed from Ukraine, and all the other random brain waves I did tweet – bounce over to Mastadon and startup an account, follow me and I’ll follow you back, and we’ll continue on like old times!

MINOR UPDATE: Dec 4th, 2022. I’m now thinking I may just delete my Twitter account soon. With the mass exodus that has occurred, the remainder of accounts seem to be an even greater cesspool of right wing, pseudo fascist, tankie, annoyances than before. I guess I could do a mass unfollow, but just nuking my account seems like an ideal thing to do. Albeit, I will probably still keep my @Adron for as long as Twitter exists. But I’m seriously leaning toward “deletion” vs. staying as a fly on the wall, there just isn’t much upside left.

Cohost

I’ve also kicked off a cohost account. Which I did this ages ago, but I’m intending to start putting actual blurbs and tidbits there, so we’ll see how that goes. It’s located here @ https://cohost.org/adron. It seems to be, at this point, a hybrid between Twitter, Mastadon, and blogging.

I’ve updated by Github Page

That’s the README.md based page located here https://github.com/Adron. It’s a neat Github feature and has all my up to date links to areas I exist in on this ole’ world wide web.

Finally, ThrashingCode Code Streaming & Videos

Ok, it’s more than just code streaming, and as is it’s been a while, but I will be getting the ole’ video vlogging going back on in the coming weeks. right now my intent is before end of year. Just like Cohost, we’ll see how that goes.

That’s where I’m at, at this point, November 9th, 2022. See all of ya out there on the interwebs. 🕸️